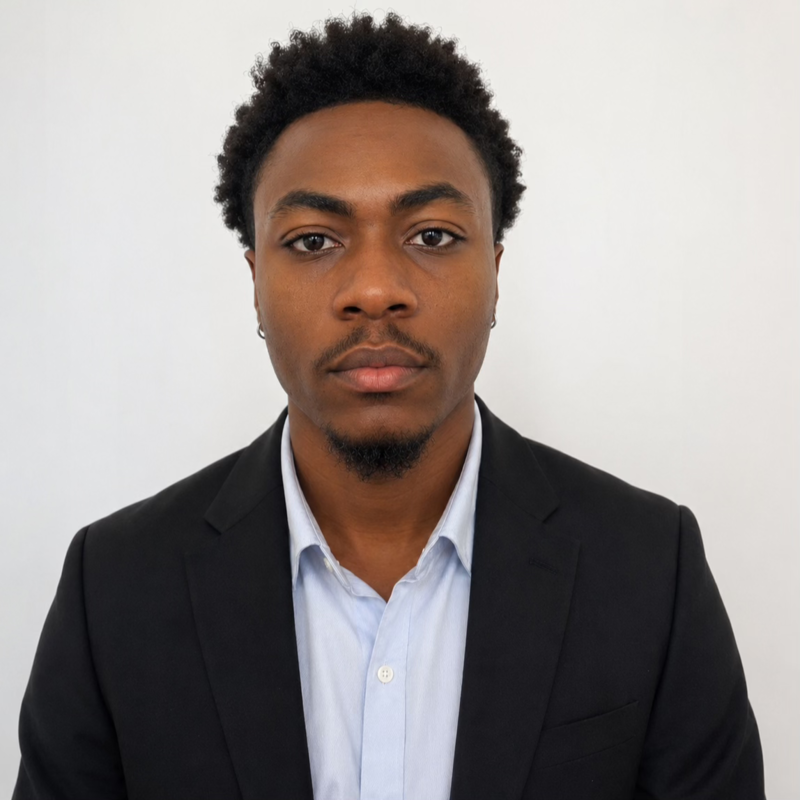
Idris Ayoade, founder of Driscop Limited, is our guest in this edition of our Ace Founder Spotlight Series.
With a robust background spanning infrastructure engineering to threat intelligence analysis, Idris saw a glaring gap in the market: millions of small businesses operate under the false assumption that they are too small to be targeted by cybercriminals.
To combat this, he teamed up with a co-founder holding a PhD in AI automation to launch Driscop, a cybersecurity startup delivering AI-driven threat detection and personalized "training nudges" directly to employees' inboxes.
I sat down with him during our cybersecurity month to discuss the very real threats facing small businesses, the story of how a single compromised email cost a business £50,000, and the crucial lessons he’s learned about prioritizing mental health and customer relationships while bootstrapping a startup.
Both questions and answers have been lightly edited for length and clarity.
The Conversation
Could you tell me something about you that most people do not know?
I spend my alone time as a solo researcher, but I also run a clothing brand on the side—more of a streetwear brand. It started as a hobby because I love fashion and art.
I spend time researching both the cyber world and what fabrics I can add to my next clothing collection. I am a lover of tech, art, and fashion.
What is your background, and how did you get into cybersecurity? My first degree was in computer science, and I worked as an infrastructure engineer for a company called CBC EMEA back in Nigeria for about two years.
From there, I moved into their cybersecurity subsidiary as a Security Operations Center (SOC) analyst, and eventually became a threat intelligence analyst.
I got fascinated by how attackers were penetrating systems and stealing data. I eventually sat down with my co-founder to address a massive problem: there are about 5.9 million SMEs in the UK, and many feel they are too small to get breached.
Yet, 20% of them get cyber-breached each year, paying up to £20,000 to remediate themselves. That motivated me to start Driscop to help SMEs train and protect themselves from phishing and smishing attacks.
How did you come up with the name Driscop?
The name came from the idea of discovering and protecting threats before they become a bigger problem.
But as I was brainstorming, playing with my own name, "Idris," it broke down into an acronym: Digital Resilience Inclusion Support, and "COP" represents something protecting you, like the police.
When the name Driscop clicked, I knew it was short, memorable, and different from the usual cybersecurity company names.
How would you explain what Driscop does?
Driscop provides cybersecurity services tailored to small businesses. We have a B2C "Training Nudge" platform with personalized modules where employees can run simulations to learn about phishing, smishing (SMS phishing), and vishing (voice phishing).
Small businesses often just do a one-year cyber awareness training and think that's enough. We encourage people to stay cyber-aware in both their workplace and personal lives. What makes us truly unique in the B2B market is our AI threat detection.
We detect suspicious files or links before they even hit your inbox and send you an instant training nudge, asking, "Are you fairly confident, very confident, or not confident at all to click this link?" We encourage people to think before they click, not click before they think.
How does that AI threat detection work in practice?
It is a user-granted access app, so you just install it into an environment like Microsoft Outlook. We don’t read the content of your messages; we analyze the network traffic for suspicious files or sender domains.
We recently spoke to a business that lost almost £50,000 before they found us. They were dealing with an overseas vendor they had trusted for 12 years. A threat actor got access to an email and waited for the right time.
They sent an invoice, but instead of the letter 'O' in the sender domain, they put a zero. The business owner came in on a Monday morning, cleared the payment, and three months later realized they never received their goods.
The bank couldn't refund the money because it was a self-initiated transaction. Anyone can fall for a cyberattack when a threat actor creates a sense of urgency, which is exactly why Driscop is here to solve that problem.
As an early-stage startup, how are you building relationships and finding your first clients?
Cybersecurity is an industry built entirely on trust. Getting someone interested is not the same as getting them to become a customer. The biggest thing for us has been listening rather than saying, "Here is our product, buy it."
We try to understand what businesses are actually struggling with and use that feedback to shape the product. We are focused on building long-term relationships rather than just chasing numbers.
What is the biggest business lesson you've learned since starting Driscop?
Learning how to prioritize. When you are an early-stage founder, you wear many hats—you are the CEO, the strategist, and the person fixing things at midnight.
There are always 10 things you could be working on, but you have to ask yourself: what is actually going to move the business forward?
I’ve learned to focus on customer feedback, product development, and building the right relationships rather than trying to do everything perfectly. If you try to do 10 things at once, you will face burnout, and you won't do any of them right. Slow and steady wins the race.
Our Closing Thoughts
Idris’s journey highlights the critical need for accessible, modern cybersecurity solutions for the underserved SME market. Key takeaways include:
SMEs are Prime Targets: Cybercriminals actively target small businesses because they often lack the massive security budgets and IT departments of larger enterprises, making them easy prey for costly invoice scams.
Contextual Training is Key: Annual compliance training isn't enough. Delivering real-time "nudges" when an employee interacts with a suspicious email builds active, daily cyber awareness.
Build on Trust: In high-stakes industries like cybersecurity, early traction comes from deep listening and customer validation, not aggressive outbound selling.
Protect Your Time (and Sanity): Founder burnout is real. Prioritizing one needle-moving task is far more effective than haphazardly trying to juggle ten.
Connect With Our Guest
Learn more at driscop.co.uk.
Follow Driscop on LinkedIn
Idris LinkedIn profile